
BSI analysis exposes limits of Windows Hello biometrics
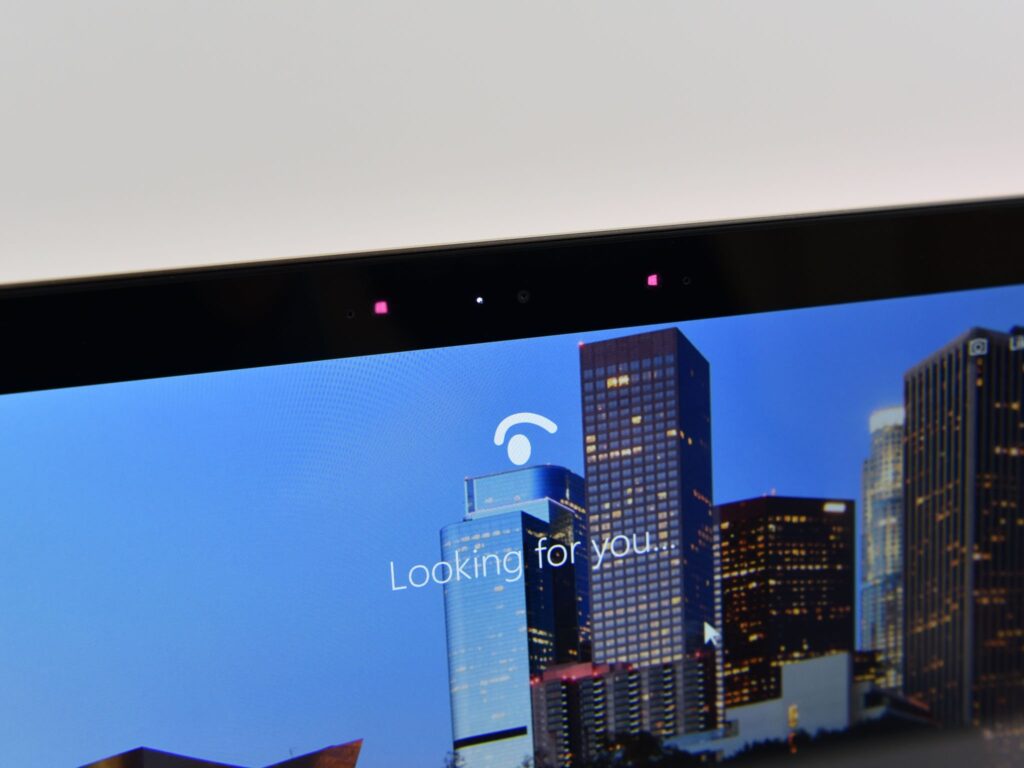
Germany’s Federal Office for Information Security has published a technical analysis from its “Windows dissected” project that analyzes how Windows Hello for Business performs biometric identification.
ERNW (Enno Rey Netzwerke) conducted the work on behalf of the BSI, using debugging and reverse engineering techniques to reconstruct internal processes.
The researchers analyzed Windows 10 Enterprise LTSC 2021 and focused on facial recognition within Windows Hello for Business.
Windows Hello for Business allows employees to sign in using a PIN, face, or fingerprint. The biometric data or PIN is checked locally, while the enterprise authentication depends on cryptographic keys associated with the device.
The private key is protected by the Trusted Platform Module (TPM).
The technology can reduce exposure to password phishing, credential theft, and remote reuse of compromised passwords because the private authentication is done on-device.
However, the study identifies limits when biometric authentication operates without Enhanced Sign-in Security (ESS).
In this configuration, the TPM may protect the key used for enterprise authentication. But it does not protect all the biometric data and processes involved in authorizing the use of that key.
The facial templates are stored in a local biometric database managed by the Windows Biometric Service. Windows restricts access to the database through file permissions and encrypts the stored templates.
However, the BSI-commissioned analysis found that this protection does not use an external secret that remains unavailable to the operating system. The information required to access the encrypted database is available on the same computer.
This separation creates a gap between protecting the authentication key and protecting the decision to allow the key to be used. An attacker may not need to extract a TPM-protected private key if they can make Windows believe that their own face belongs to an authorized user.
A privileged attacker could attempt to modify enrollment records in the biometric database.
Each enrolled biometric record is connected to a Windows security identifier (SID), which tells Windows which user account corresponds to the template that produced a successful match. If an attacker can change that association, the biometric system could recognize one person’s face but return another user’s identity.
The report’s concern is around what happens after an attacker has obtained substantial control of the local Windows device. Under that threat model, the security of the biometric template database, matching process, and identity mapping becomes important.
ESS changes the biometric security boundary
Enhanced Sign-in Security changes the Windows Hello architecture by moving sensitive biometric operations away from the normal Windows environment. ESS introduces an additional isolation boundary built around Virtualization-based Security, TPM 2.0, and compatible biometric hardware.
The BSI report’s facial recognition tests raise a different issue from these local administrator attacks. They analyzed what the facial recognition system accepts at the sensor during enrollment and later authentication.
The researchers observed that Windows Hello allowed them to enroll a facial mask in place of a real face. After creating the enrollment, they were able to authenticate using another mask depicting the same person.
The report presents this as a presentation attack. The system accepted an artificial representation during setup and later treated another version of that representation as a valid match.
The researchers also tested the effect of degraded enrollment conditions.
In one experiment, a person registered for facial recognition while wearing a scarf, glasses, and a hood. Another individual wearing the same combination of accessories was able to authenticate.
When the original user completed enrollment without reduced facial visibility, the researchers were no longer able to reproduce the incorrect acceptance.
These observations show that the security of facial authentication can also be affected by the quality of the biometric sample accepted during enrollment.
The BSI report provides practical measures for reducing the risks that arise when biometric identification is used to authorize access to device bound enterprise credentials.
The lesson for enterprises is that the protection depends on how the device is configured, which biometric hardware is installed, who is allowed to enroll, how local administrator access is controlled, and whether the biometric process is isolated through Enhanced Sign-in Security.
Related Posts
-
 August 8, 2025
-
 May 25, 2026
-
 January 23, 2026
-
 July 14, 2026
-
 April 29, 2026
-
 October 10, 2025
Article Topics
biometric authentication | biometrics | cybersecurity | Enhanced Sign-in Security | Windows Hello

Comments