
The death of the pixel: Why cryptographic provenance is the next identity frontier
By Udi Abram, VP of Corporate Affairs, AU10TIX
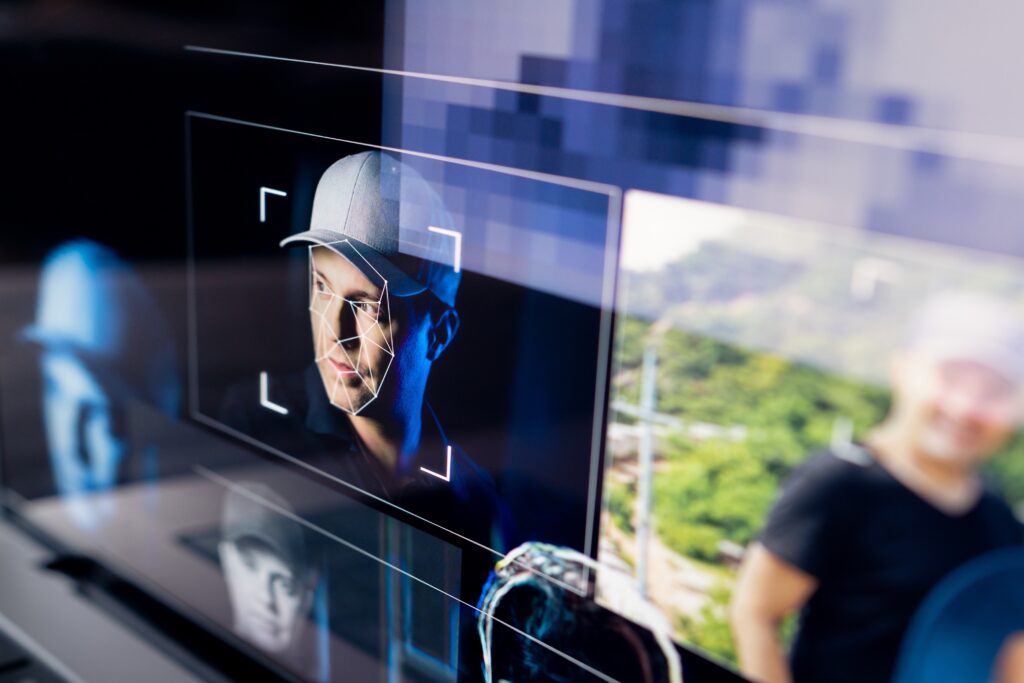
For years, digital identity verification rested on a straightforward assumption: if a face appears to be real on camera, it probably is.
Generative AI has broken that assumption.
Fraudsters increasingly have access to virtual cameras, emulators, compromised devices and techniques to manipulate the data an application receives. In an injection attack, synthetic or manipulated media can be introduced directly into an identity verification flow rather than presented to a physical camera. The verification system may believe it is examining a person captured by a device sensor. What it is actually evaluating is a manufactured signal.
The pixels may look convincing. Their origin is the problem.
The rise of injection attacks
For years, the cybersecurity industry focused on presentation attack detection, making sure someone wasn’t holding a rubber mask or an iPad up to their webcam. But generative AI changed the math entirely. Today, organized crime rings use virtual emulators and root-level device hacks to hijack the application’s API. We call these injection attacks.
These attacks intercept the data feed and inject a flawless, real-time, AI-generated video clone directly into the bank or crypto app. The software is analyzing the video feed, thinking it’s verifying a live human making micro-expressions, but it’s actually authenticating a synthetic ghost. The pixels are perfect, but the provenance is completely fake.
This has become such a systemic, global crisis that regulators are finally stepping in. We are seeing major regulatory bodies in the US and Europe scrambling to address the issue and looking at updates to NIST digital identity guidelines and the rollout of eIDAS 2.0. It is no longer enough to rely solely on liveness detection that asks, “Does this look like a real person?” The new compliance mandate is about cryptographic provenance: “Can you prove mathematically that this video feed originated from the physical hardware of a trusted device?”
If an enterprise is still just looking at the pixels and ignoring device-level telemetry, they aren’t just vulnerable to fraud; very soon, they will be completely out of compliance.
When the image is no longer evidence
This is what I call the “death of the pixel”, the erosion of visual information as sufficient evidence of authenticity. When pixels can be manufactured on demand, staring harder at them is a losing strategy. The deepfake will eventually beat every deepfake detector, because both sides are training on the same technology (and the attackers will always iterate faster).
As generative technology improves, organizations cannot assume that increasingly sophisticated image analysis will always determine whether an image represents reality. Detection remains important, but there is an inherent weakness in making the artifact itself the primary source of truth.
A useful analogy is the authentication of a valuable watch. A sophisticated counterfeit may look indistinguishable from the real deal. An expert, therefore, does not rely solely on appearance alone. They examine the serial number, manufacturer records, documentation and chain of custody to prove that the watch is legit. Because if they don’t, the financial and reputational damage they might face if a fake watch enters their inventory is enormous.
That is the significance of cryptographic provenance: verifying the chain of custody of the signal itself including hardware attestation, device integrity and sensor-level evidence, alongside behavioral telemetry that no emulator can convincingly reproduce. A real human hand has a tremor. A server rack does not.
From pixels to provenance
Building toward cryptographic provenance doesn’t require the complete overhaul of identity infrastructure overnight. For executives, the practical takeaway fits into three questions:
- Can your verification provider detect an injection attack (not a mask, an injection) and can they evidence it?
- Does your tech stack collect device and sensor-level attestation, or does it only analyze the image it is handed?
- When a regulator or enterprise customer asks how you know a session began with a real human on a real device, is the answer a mathematical proof or a probability score?
The pixel had a good life. For 20 years, it was the industry’s witness, serving honestly until generative AI taught it to lie. Provenance is the new witness and, unlike the pixel, it can take the stand.
The next era of digital identity will therefore be defined not by how closely organizations can inspect what they see, but by how confidently they can prove where it came from.
About the author
Udi Abram is VP of Corporate Affairs at AU10TIX.
Related Posts
-
 March 19, 2026
-
 January 22, 2026
-
 March 24, 2026
-
 September 16, 2025
-
 May 21, 2026
-
 July 8, 2026
Article Topics
AI fraud | AU10TIX | continuous authentication | cryptography | cybersecurity | digital identity | identity orchestration

Comments