
Why a strong credential is only the start of the trust chain
By Henry Patishman, Executive Vice President, Identity Verification Solutions at Regula
In the span of a single week, two separate cybersecurity events offered a peek of the changes ahead.
The first was a reported vulnerability affecting software within Belgium’s national eID authentication ecosystem. The second was an AI-assisted campaign against Taiwanese government systems, targeted by multiple agents apparently working in parallel to identify systems, research vulnerabilities, and adjust their tactics when an approach failed.
One case was about the infrastructure around a trusted digital credential. The other demonstrated how AI enables attackers to increase the speed, scale, and flexibility of a cyberattack. Together, they suggest a new security reality: digital identity is becoming critical infrastructure at the same time that attackers are gaining more capability to analyze it.
A strong credential is just a part of the entire transaction
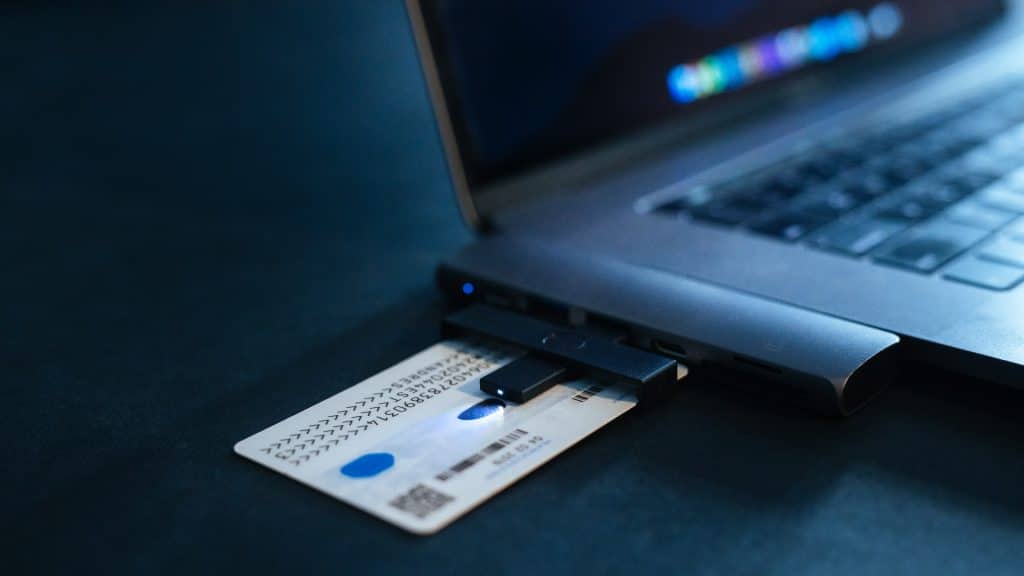
Belgium’s eID is more than a login method. It is a national, chip-based credential used to access public services and sign documents electronically. That is what makes a vulnerability in the surrounding software significant. It should not be seen as evidence that the eID or its cryptography was broken; rather, it shows that even a strong credential depends on the systems used to process and accept it.
While a government-issued eID provides robust evidence of a valid credential being presented, the transaction is also dependent on the software that runs the credential, the service that validates and communicates the authentication, and the application that uses that to establish a session and grant access.
Each of these components delivers a different security capability. A vulnerability within one does not necessarily mean the cryptographic integrity of the credential has been undermined but it does mean the security of the entire transaction may be impacted. A high-assurance credential does not mean a high-assurance journey from presentation to access.
This distinction is becoming important as digital identity develops into infrastructure. The same credential may soon connect individuals to government, finance, health, and commerce services. There are clear security and usability benefits to be had. But that also means the infrastructure needs to be protected with a level of assurance proportionate to the trust placed in the credential.
The takeaway is not that digital identity creates insecurity. It is that the strength of the credential raises the security requirements for systems that rely on it.
Autonomous attacks change the economics
The attack on Taiwan illustrates the other side of the shift. Taiwan’s Ministry of Digital Affairs confirmed that the operation combined manual hacking with AI-agent-assisted techniques. According to Dream researchers, up to eight agents mapped 21 government systems, compromised at least 85 accounts, and extracted more than 2,500 personnel records.
This was not a wholly automated attack. Someone still chose the targets, defined the goals, and launched the operation. What has changed is the amount of work that could be offloaded.
Tasks like reconnaissance, vulnerability research, and running through multiple attack vectors have historically required time, specialist knowledge, and coordination. AI agents can perform parts of that work in parallel. An individual skilled operator can then deliver the speed and scale of an attack previously performed by a much larger attack team.
This of course changes the economics of cyberattacks. More systems can be examined, more hypotheses tested, and more variations attempted at a lower cost. When one path is blocked, an agent can find another rather than looping back to the same original attack approach.
Those compromised accounts and personnel records are what connect the campaign directly to identity security. Once attackers control a trusted account, what they do next may no longer look like an external intrusion. It may look like activity from a user the system has already authenticated.
Attackers don’t necessarily need to attempt the strongest credential or break the strongest barrier. They can find a weaker point elsewhere in the process and leverage the trust already afforded to an identity.
When these trends meet
The two events highlight different sides of the same coin. Digital identity ecosystems are becoming more interconnected, while AI-assisted attackers are becoming better equipped to examine complex systems. Complexity that once slowed an attacker may now provide an AI agent with more possible paths to investigate.
This trend is already evident in identity verification. Regula’s latest research found that 35% of organizations were unsure whether activity within their identity processes was from a human or automation. As legitimate customers, authorized AI agents, malicious bots, and human-directed attack tools begin interacting with the same systems, determining who – or what – is behind an action will become more difficult.
Organizations must start evaluating identity assurance end-to-end. That means not only confirming that identity evidence is authentic, valid, and associated with the person presenting it but also having a trusted capture and processing environment to ensure genuine evidence cannot be substituted, replayed, or injected into the verification flow.
Trust should also be recalibrated when the risk shifts. Account recovery, credential reset, device change, privilege elevation, and sensitive transactions may require fresh evidence to associate an action with the identity holder. The goal is not to repeat full identity verification continuously, but to get evidence proportionate to the specific doubt.
No single technology can protect all layers. Document and biometric verification, credential processing, application security, session protection, and access management answer different questions. The level of assurance comes down to how these capabilities complement and reinforce one another.
The solution is not less digital identity. Digital IDs, chip-enabled documents, biometrics, and wallets offer substantially stronger assurance than passwords or self-declared data. The next challenge is to preserve that assurance beyond the credential – from initial verification through every high-risk interaction.
A strong credential needs to be treated as the foundation of the trust chain, not the final link.
About the author
Henry Patishman is Executive Vice President of Identity Verification Solutions at Regula.
Related Posts
-
 June 25, 2026
-
 December 8, 2025
-
 October 20, 2025
-
 July 22, 2026
-
 July 15, 2026
-
 March 10, 2026
Article Topics
cybersecurity | digital identity | digital trust | Regula

Comments