
A biometric system can be accurate and still fail an accessibility test
By Joshua W.J. Brown
Biometric authentication has mature ways to talk about comparison error. That is exactly why accessibility failures should not be folded into a vague complaint about a system’s “accuracy.” False match rate and false non-match rate describe consequential things, and current NIST guidance treats them separately. The harder accessibility question often sits outside the comparison score: can the legitimate user produce a usable biometric sample in the first place, and if not, can that user recover independently at equivalent assurance?
That distinction matters because a technically strong matcher can sit inside an inaccessible authentication journey. ISO/IEC 19795 already recognizes failure to acquire: the capture and feature-extraction process does not produce biometric features suitable for comparison. The same performance framework also distinguishes failure to enroll from false accepts and false rejects. In other words, the standards vocabulary already gives us a clue: some authentication failures happen before a matcher can make the decision people usually call “accuracy.”
Current NIST Digital Identity Guidelines make the operational consequence explicit. For federal authentication systems, biometrics are supported only as part of multi-factor authentication with a physical authenticator, and an alternative non-biometric option must always be available. NIST also says a single authenticator type will not usually serve an entire user population and recommends alternative authenticator types that users can choose according to their needs and context.
Accessibility standards make the same point from another direction. Canada’s CAN/ASC-EN 301 549:2024 says that when ICT uses biological characteristics, it must not rely on one particular biological characteristic as the only means of identification or control. The reason is practical: a fingerprint, face, iris, voice or other modality is not equally usable by every person in every context.
Choice does not have to mean lower assurance. W3C’s explanatory guidance for WCAG 2.2 Accessible Authentication uses WebAuthn as one example: the relying party can authenticate through a device while the device may let the user choose a face scan, fingerprint or PIN. The credential can remain strong without forcing every legitimate user through the same human-device interaction.
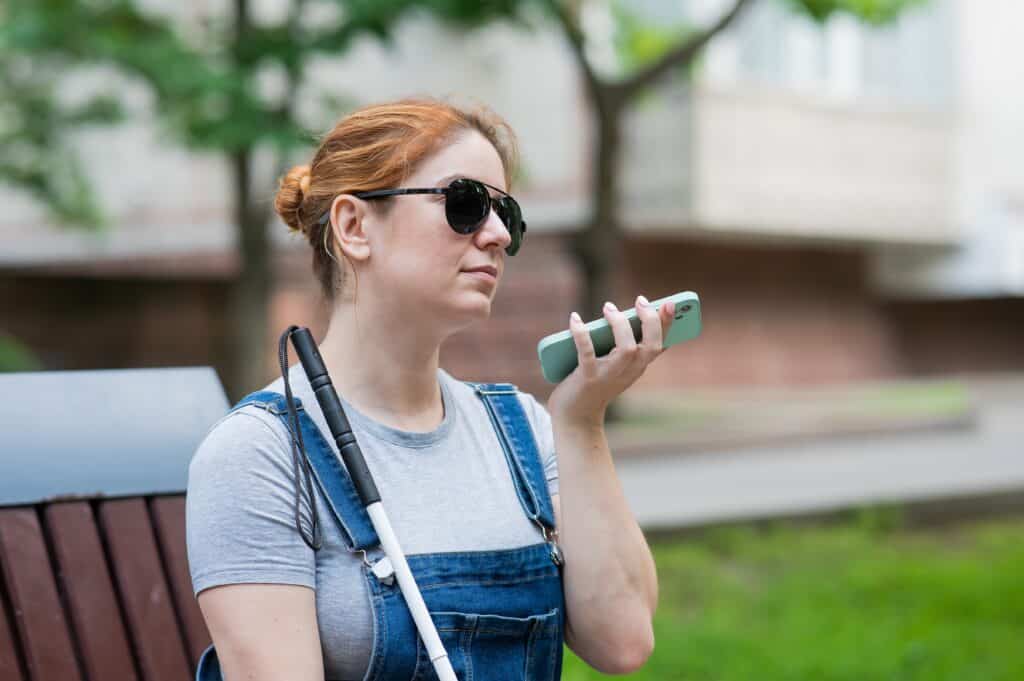
The evidence from financial services shows what happens when that design principle is ignored. A 2026 Journal of Medical Internet Research scoping review examined 23 studies of digital financial applications used by people with visual impairment. Authentication-related barriers appeared in 18 studies; biometric authentication that was not consistently accessible appeared in nine. The review also found users relying on sighted assistance for login, verification and payments, compromising privacy and independent financial control.
This is where a high-level authentication success figure can become misleading even when the underlying biometric accuracy reporting is sound. A bank can know its face matcher’s false match and false non-match characteristics and still lack a useful operational answer to a different question: what happens to the legitimate customer who cannot complete the face flow? If the fallback is buried, inaccessible, slower by an order of magnitude, weaker than the primary method, or dependent on another person taking control of the device, the system has not merely created friction. It has changed the security and privacy properties of authentication for that user.
Biometric programs therefore need an accessibility layer in operational telemetry. This should not mean inferring disability from a failed scan. That would create a new privacy problem. Instead, providers can instrument the authentication journey around observable events and voluntary user choices: modality attempted; acquisition or comparison failure class; alternative offered; alternative selected; assurance level of the alternative; time to recovery; whether the user completed recovery without third-party assistance; and final outcome. An optional, privacy-preserving accessibility exception flag can be user-declared rather than guessed by the system.
Four measures would make those logs much more useful. First, report failure-to-acquire alongside comparison errors where the deployment can observe it. Second, track alternative-path availability: after a failed or unusable biometric step, was an equivalent route actually offered? Third, measure independent recovery: what proportion of legitimate-user failures were resolved without another person handling credentials, secrets or transaction control? Fourth, record recovery time and abandonment, because an alternative that exists only after a twenty-minute support escalation is not operationally equivalent to a two-second face or fingerprint check.
None of these measures replaces FMR, FNMR, presentation-attack testing or demographic performance analysis. NIST’s ongoing Face Recognition Technology Evaluation continues to show why those measures matter: false positives and false negatives can vary across demographic groups, and false negatives are sensitive to image quality, including capture conditions such as lighting and camera positioning. The point is additive. Comparison performance asks whether the biometric decision is correct given a usable sample. Accessibility performance asks whether the person can reach that decision point and recover securely when the modality does not work for them.
This also gives procurement teams a better question than “Does the product support biometrics?” Ask for the complete legitimate-user failure path. What counts as failure to acquire? What happens after repeated capture failures? Can the user select another authenticator before being locked out? Does the alternative satisfy the same assurance requirement? Is it accessible with assistive technology? Can the person complete it privately? Are those events measured in production rather than demonstrated once in a sales environment?
The goal is not weaker identity assurance. It is equivalent assurance through more than one usable path. Biometrics can reduce friction and strengthen authentication for many people. But a system should not count a user as an edge case simply because the primary modality cannot acquire them reliably. The mature way to measure biometrics is already multi-dimensional. Accessibility should be treated the same way: not as a slogan attached to an aggregate pass rate, but as a measurable property of the authentication system from first capture through successful, independent recovery.
Related Posts
-
 July 8, 2026
-
 June 17, 2026
-
 August 13, 2026
-
 January 8, 2026
-
 May 25, 2026
-
 July 6, 2026
Article Topics
accessibility | biometric authentication | biometric matching | biometrics | identity assurance

Comments