
Aware CCO pitches NIST Digital Identity Guidelines at Identity Week
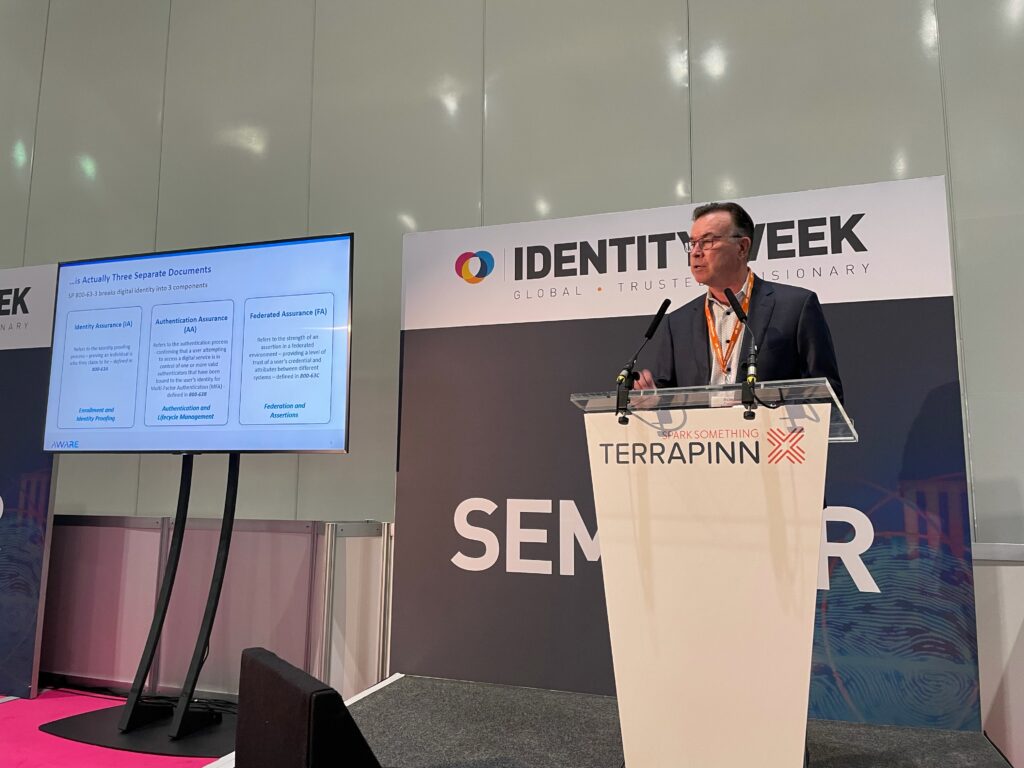
New proposed guidelines from the U.S. National Institute of Standards and Technology (NIST) were promoted to an international audience in London by Aware CCO Rob Mungovan.
He described it as a government’s attempt to define the concepts of digital identity, best practices and suggestion of mandatory requirements at the federal level. The capacity for incorporating biometrics at the higher levels could make digital identity more convenient with support for passwordless authentication and remote identity proofing.
NIST Special Publication 800-63-3, a series of standards for enrolment and identity proofing – proving an individual is who they claim to be, authentication – checking a user attempting digital access is in control of one or more authenticating factors in a Multi-Factor Authentication situation, and federation assertion – providing a level of trust of a user’s credential between different systems (federated environments).
Mungovan broke down the requirements for the various standards, pointing out how biometrics are only mandatory for the strictest standard, level three.
The system stipulates that no more than five consecutive failed authentication attempts are permitted, or 10 consecutive failed attempts if biometric presentation attack detection (PAD) is in use, and a false match rate in facial recognition of just 1 in 1,000.
Mungovan pointed out that NASA recently introduced remote identity proofing in line with the guidelines, in partnership with Idemia. The space agency’s move came as something of a surprise, but the release of NIST standards “feels different.” He believes much large government departments will follow soon and other countries have expressed interest in adopting the guidelines. The Department of Veterans Affairs adopted remote identity proofing from ID.me in line with the guidelines in February, 2019.
Aware’s Knomi platform has been developed to allow government agencies to provide remote onboarding, up to level 2 of the standards. The company is seeing strong adoption in Latin America and Turkey.
This post was updated at 3;20pm on September 27, 2021 to clarify that NASA’s implementation of NIST 800-63 IAL2 is not the first by the U.S. government.
Related Posts
-
 August 22, 2024
-
 February 26, 2025
-
 September 11, 2024
-
 November 20, 2024
-
 July 2, 2024
-
February 28, 2025
Article Topics
Aware | biometrics | digital identity | IAL2 | identity verification | Identity Week | NIST | NIST Special Publication 800-63 | remote authentication | standards

Comments