
Kaspersky finds critical vulnerabilities in ZKTeco biometric access control terminal
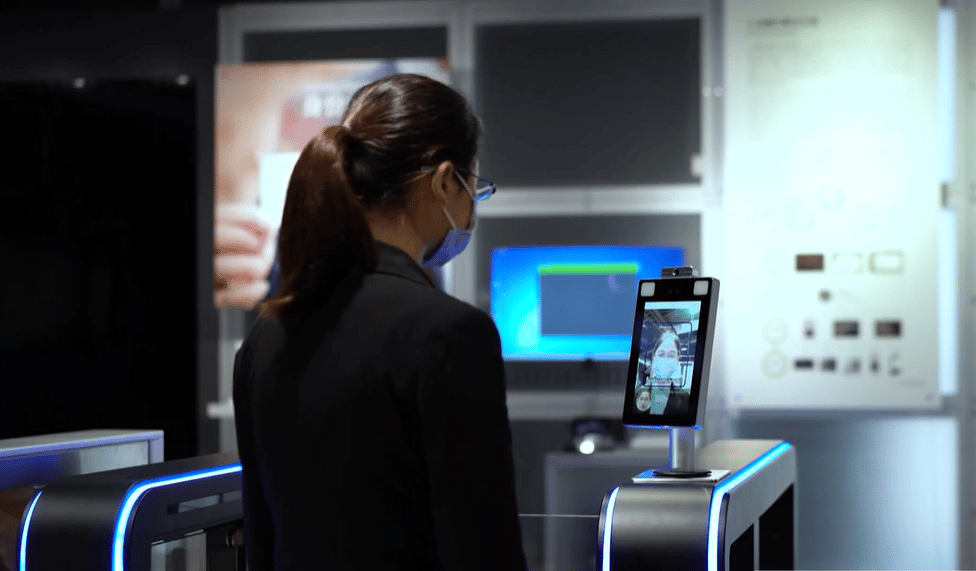
Kaspersky says there is a set of cybersecurity vulnerabilities in biometric access control terminals from ZKTeco that could allow malicious actors to bypass verification to gain unauthorized access, steal biometric data, and even deploy backdoors to user networks.
The hybrid biometric terminal is a white-label product sold under different names by different distributors, according to Kaspersky’s announcement. It enables access control via authentication with face biometrics or QR codes. They are used in many environments, Kaspersky says, including high-security facilities like nuclear power plants, and they can store thousands of facial templates.
ZKTeco is among the largest suppliers of biometric access control hardware in the world, with subsidiaries in several countries and ties to Armatura.
Five sets of vulnerabilities, 24 in total, have been registered as Common Vulnerabilities and Exposures (CVEs) by Kaspersky. CVE-2023-3938 through CVE-2023-3943 could allow criminals to defeat or misuse ZKTeco biometric access control systems in several ways.
The first allows SQL injection attacks, which can in turn be used to impersonate the most recent legitimate user, restart the device, or in combination with other vulnerabilities, download enrolled users’ photos and reuse them for presentation attacks. ZKTeco’s terminal includes warmth detection as a defense against presentation attacks, but a Kaspersky analyst says it is still a threat with significant potential.
Another vulnerability allows attackers to read or extract any file in the system, including biometric data and password hashes. A third allows the retrieval of sensitive information on users and the system, also through SQL injections.
The biometric database can be altered by yet another vulnerability, allowing attackers to pose as legitimate users or simply add unauthorized individuals to the database. Two final groups of vulnerabilities enable attackers to execute commands and take control of the device, Kaspersky says. From there, attacks can be launched on other network nodes.
“The ability to alter the database weaponizes the original purpose of the access control devices, potentially granting access to restricted areas for nefarious actors,” comments Kaspersky Senior Application Security Specialist Georgy Kiguradze. “Lastly, some vulnerabilities enable the placement of a backdoor to covertly infiltrate other enterprise networks, facilitating the development of sophisticated attacks, including cyberespionage or sabotage. All these factors underscore the urgency of patching these vulnerabilities and thoroughly auditing the device’s security settings for those using the devices in corporate areas.”
Kaspersky recommends isolating the biometric devices in their own network segment, change default passwords and put more robust ones in place, auditing security settings like the warmth liveness detection capability, minimize the use of QR codes and update the firmware regularly.
Biometric Update reached out to ZKTeco for comment and will update this story when we hear back.
Related Posts
-
 February 20, 2024
-
 August 10, 2023
-
 December 6, 2023
-
 March 28, 2024
-
 March 22, 2024
-
March 6, 2024
Article Topics
access control | biometrics | cybersecurity | face biometrics | injection attack detection | Kaspersky Lab | ZKTeco

Comments